AI-Powered Cyberattacks Take Center Stage as Palo Alto Networks Prepares to Unveil New Security Technology
Artificial intelligence is rapidly changing the cybersecurity battlefield, and the next stage of that contest is moving beyond AI-assisted attacks toward increasingly automated cyber operations.
That shift is putting new pressure on security teams that have traditionally relied on detecting threats, investigating alerts, and patching vulnerabilities after they become known.
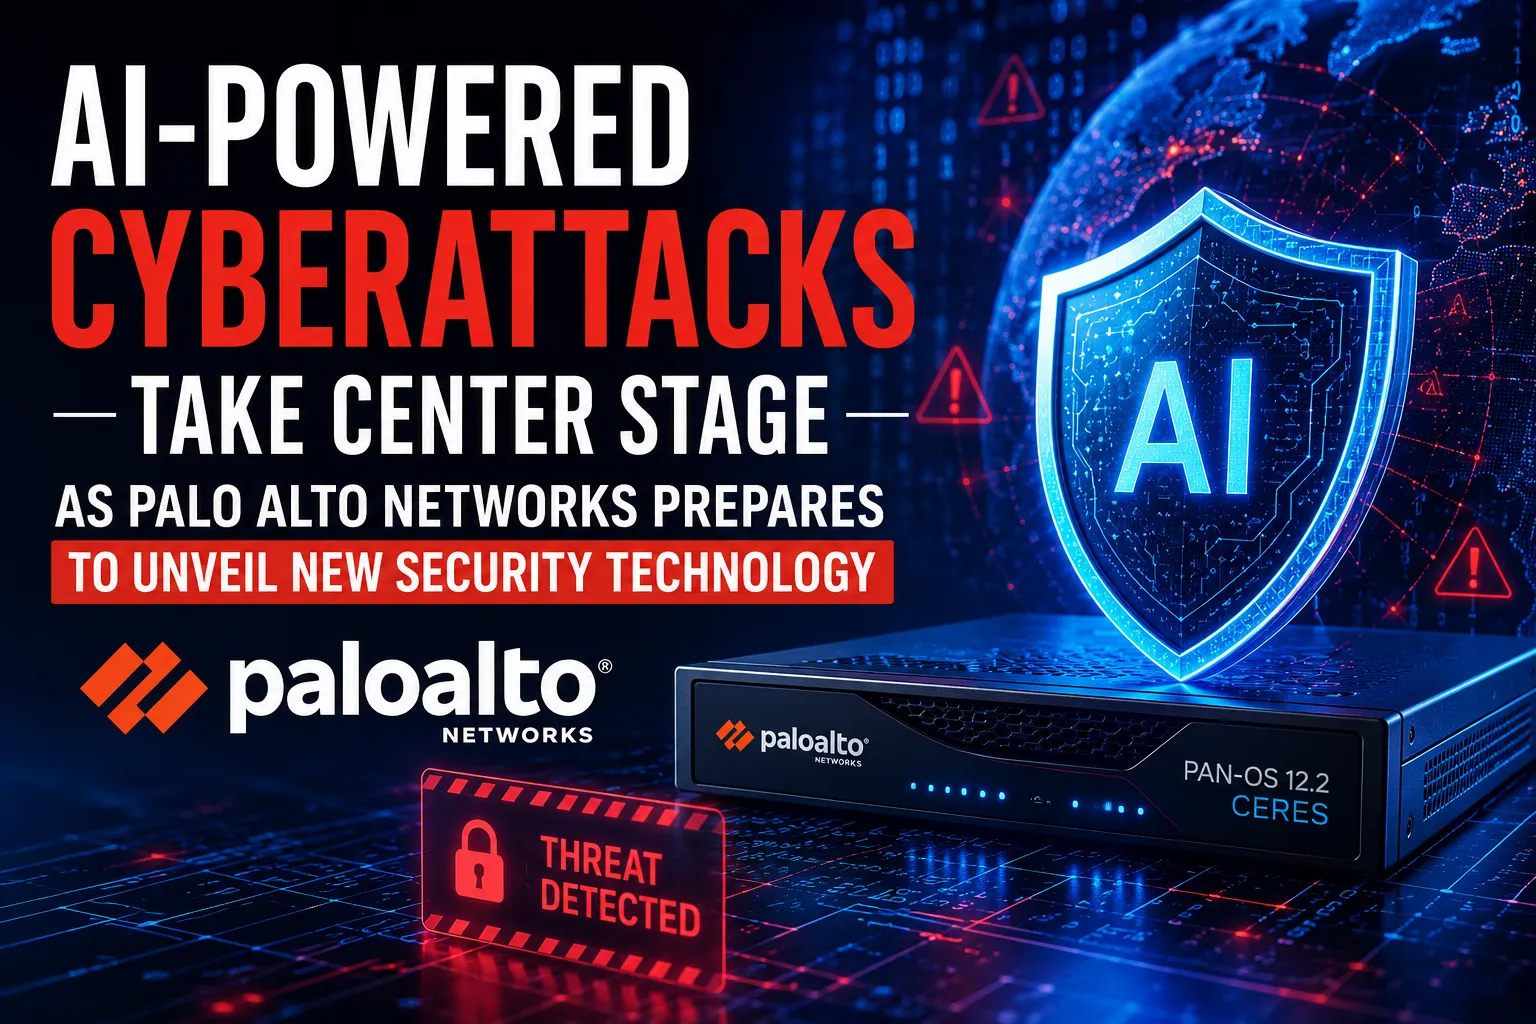
Against that backdrop, Palo Alto Networks is preparing to showcase a new generation of network-security technology at its InterSECt 2026 event, where the company has announced plans to reveal PAN-OS 12.2 Ceres. The virtual event is scheduled for August 19 in the Americas and August 20 for Europe, the Middle East and Africa and Asia-Pacific. (Palo Alto Networks)
The announcement comes as cybersecurity researchers warn that advanced AI is shortening the amount of time organizations have to respond to vulnerabilities and attacks.
AI Is Changing the Speed of Cyberattacks
Cybercriminals have used automation for years, but frontier AI is introducing a different level of capability.
AI models can assist with reconnaissance, vulnerability discovery, coding, phishing, scripting, and other parts of an attack. The result is a potential shift from attacks that require substantial human involvement to campaigns in which software performs more of the work.
Palo Alto Networks’ Unit 42 says its 2026 incident-response research found that the fastest attacks it investigated moved from initial access to data exfiltration in as little as 72 minutes—four times faster than the previous year. The company also found that identity-related techniques played a major role in incidents it investigated. (LIVEcommunity)
The significance is straightforward: security teams may have less time to recognize an intrusion and stop it before sensitive information or systems are affected.
The Patch-and-Respond Model Faces New Pressure
For decades, software patching has been one of the fundamental ways organizations respond to newly discovered vulnerabilities.
A vulnerability is identified, a software vendor develops a fix, organizations test the update, and security teams deploy it.
That process remains important, but AI-powered vulnerability discovery could make the gap between discovery and exploitation increasingly difficult to manage.
Palo Alto Networks says its autonomous research system, called NOVA, analyzed 3,915 open-source software projects in two months and identified 14,090 confirmed vulnerabilities. The company said 99.4% had not previously been reported and about 40% were rated high or critical severity. (Unit 42)
The research illustrates the scale of what automated vulnerability discovery can produce.
It also highlights a fundamental problem for defenders: finding vulnerabilities faster is useful to everyone—including attackers.
What Palo Alto Networks Is Expected to Showcase
Palo Alto Networks has positioned InterSECt 2026 around what it describes as the future of “Frontier AI network security.”
The company says PAN-OS 12.2 Ceres is designed to move network defense further upstream, with the objective of reducing exposure before attacks are launched. Its event materials specifically point to AI-enabled attackers discovering vulnerabilities at scale and producing customized exploits at machine speed. (Palo Alto Networks)
Palo Alto Networks’ technical documentation now lists several capabilities associated with Ceres, including:
- Advanced Virtual Patching
- Advanced IP Defense
- Network Security Agents
- Post-quantum cryptography for GlobalProtect
- Intent-based configuration management
- Proactive OT microsegmentation
- NGFW-native Prisma Browser identification
- Threat Prevention protections for GlobalProtect
The company describes the release as combining autonomous AI-driven security operations with defenses designed for evasive and AI-powered threats. (Palo Alto Networks TechDocs)
Virtual Patching Could Become More Important
One of the more significant ideas behind the new approach is virtual patching.
Traditional patching requires the underlying software to be updated. Virtual patching, by contrast, can use security controls to block exploitation of a vulnerability before the vulnerable application itself receives a permanent software fix.
That distinction could become increasingly valuable when attackers are able to move quickly after a vulnerability becomes known.
Palo Alto Networks has highlighted Advanced Virtual Patching as part of its Ceres approach, positioning it as a way to identify and protect against vulnerabilities before attackers can weaponize them. (Palo Alto Networks TechDocs)
For businesses with large and complicated technology environments, that could be particularly important.
Organizations may operate thousands of applications, devices, cloud workloads, remote connections, and third-party services. Updating every component immediately is often difficult.
A security layer capable of providing temporary protection while permanent fixes are prepared could therefore reduce exposure during that gap.
Blocking Attack Infrastructure Before the Attack
Another major focus is the infrastructure attackers use to conduct campaigns.
Cyberattacks typically require more than malicious software. Attackers may need servers, domains, IP addresses, command-and-control infrastructure, proxies, and other resources to communicate with compromised systems.
Palo Alto Networks says its Advanced IP Defense capability is designed to identify and block attacker infrastructure before it can be used against an organization.
The company’s documentation says the system uses real-time Precision AI intelligence, Zero Trust DNS validation, and numerous security attributes associated with public IP addresses to identify higher-risk traffic. (Palo Alto Networks TechDocs)
The underlying philosophy is different from simply waiting for malicious activity to reach an endpoint.
Instead, the defense attempts to prevent the connection from being established in the first place.
Network Security Agents Could Extend Automation
AI agents are becoming an important part of the broader technology industry, and cybersecurity is no exception.
Traditional security operations centers depend heavily on analysts to investigate alerts, correlate information, determine severity, and decide what action to take.
That model can become difficult to scale when the number and speed of threats increase.
Palo Alto Networks says Ceres introduces Network Security Agents intended to scale network-security operations beyond human limits. (Palo Alto Networks TechDocs)
The potential advantage is speed.
An automated security agent can continuously process information and take predefined actions without waiting for an analyst to manually investigate every event.
However, automation also introduces questions about control, accuracy, authorization, and the consequences of an incorrect action.
AI Is Becoming Both Weapon and Shield
The cybersecurity industry increasingly faces an unusual technological competition.
The same broad category of AI capabilities can help attackers and defenders.
Attackers can use AI to analyze targets, generate malicious code, search for weaknesses, personalize phishing attempts, and automate parts of an operation.
Defenders can use AI to analyze massive volumes of security data, identify unusual behavior, prioritize vulnerabilities, automate investigations, and respond more quickly.
This has created an emerging philosophy within cybersecurity: fight AI with AI.
Palo Alto Networks itself describes its Precision AI technology as combining machine learning, deep learning, and generative AI capabilities to provide real-time security against increasingly automated threats. (Palo Alto Networks)
The competition is therefore not simply about who has the better AI model.
It is increasingly about who can connect AI to useful security data, reliable controls, automated response systems, and a broader security infrastructure.
Why Human Analysts Still Matter
Greater automation does not mean cybersecurity teams can simply hand their responsibilities to AI.
Security decisions can have serious consequences.
Automatically blocking a malicious connection may be beneficial, but automatically shutting down a legitimate business system could create its own disruption.
AI systems can also make mistakes, misunderstand context, or respond to incomplete information.
Human oversight therefore remains important, particularly for high-impact decisions.
The most practical future may involve AI handling large volumes of routine detection and response work while human security professionals focus on unusual cases, strategic decisions, risk management, and oversight.
Identity Is Becoming a Major Security Target
AI-driven attacks are not only about exploiting software vulnerabilities.
Identity has become another critical component of the modern threat landscape.
Palo Alto Networks’ 2026 incident-response research found that identity-based techniques were involved in nearly 90% of the investigations covered by its report. The company said attackers increasingly use stolen credentials and tokens to access systems and then escalate privileges or move laterally. (LIVEcommunity)
This matters because an attacker who already possesses valid credentials may not need to break through a traditional perimeter in an obvious way.
The activity can look more like legitimate access.
As businesses deploy AI agents, cloud applications, remote work platforms, and interconnected services, identity management becomes even more important.
AI Agents Create a New Security Problem
The rise of autonomous AI agents introduces another layer of complexity.
Traditional software generally waits for instructions from a user or another program. AI agents can be designed to interpret goals, use tools, access information, and perform multi-step tasks with less direct human involvement.
That can be extremely useful for businesses.
But an agent with excessive permissions can also become a security risk.
Palo Alto Networks has previously warned about risks involving agentic AI, including agent identity, runtime security, automated governance, and “Shadow AI”—AI tools used within organizations without appropriate security oversight. Its Prisma AIRS 3.0 platform was introduced in March 2026 to address security across the agentic AI lifecycle. (Palo Alto Networks Investors)
The security challenge is therefore expanding from protecting computers and networks to protecting the actions performed by autonomous software.
The Attack Surface Is Expanding
AI is being integrated into almost every part of the technology environment.
Businesses are deploying AI assistants, coding tools, customer-service systems, data-analysis platforms, autonomous agents, and AI-powered applications.
Each new system can create additional connections, identities, data flows, and permissions.
That can increase productivity, but it also expands the attack surface.
An organization may now have to consider not only whether a laptop or server is secure, but also:
- Which AI tools employees are using
- What information those tools can access
- Which agents can execute actions
- What permissions AI systems have
- How AI-generated code is secured
- Whether third-party AI services are trustworthy
- How AI activity is monitored
- What happens if an AI agent is manipulated
Cybersecurity is consequently becoming part of the AI adoption process rather than something added afterward.
The Shift From Detection to Prevention
Perhaps the most important idea behind the Ceres announcement is the move from reactive security toward prevention.
Traditional security often revolves around a familiar sequence: detect an alert, investigate it, determine whether it is malicious, and respond.
That approach becomes increasingly difficult if an automated attack can complete critical steps faster than humans can investigate alerts.
Palo Alto Networks is arguing for a different model: identify vulnerabilities, attacker infrastructure, and other indicators of risk early enough to prevent the attack from reaching its intended target. (Palo Alto Networks)
The distinction may become increasingly important as AI accelerates both sides of the cybersecurity equation.
Businesses Face a Difficult Balancing Act
For businesses, the rise of AI-powered cyberattacks creates two competing priorities.
They need to adopt AI quickly enough to remain competitive.
At the same time, they need to prevent new AI deployments from becoming security weaknesses.
Moving too slowly can mean missing productivity opportunities. Moving too quickly without adequate controls can expose sensitive data, systems, and intellectual property.
This makes security architecture increasingly important.
Rather than treating AI security as an isolated product category, companies may need to integrate security controls into the way AI systems are designed, deployed, monitored, and updated.
Why the Palo Alto Announcement Matters Beyond One Product
Palo Alto Networks is only one company operating in a much larger cybersecurity market.
Other major security vendors are also investing heavily in AI-powered detection, autonomous security operations, identity protection, cloud security, and automated response.
The significance of the Ceres announcement therefore extends beyond the specific features of one firewall platform.
It reflects a wider industry transition.
Cybersecurity companies are increasingly designing systems for a world in which attackers can discover vulnerabilities, generate tools, and coordinate attacks at speeds that human teams cannot match manually.
The competitive question is becoming whether defenders can automate faster than attackers.
What Security Teams Should Watch
As AI-powered threats evolve, organizations will likely pay closer attention to several areas.
Vulnerability Exposure
Knowing which systems are vulnerable is no longer enough. Organizations need to understand which vulnerabilities are exposed to attackers and which require immediate action.
Identity Security
Credentials, tokens, privileges, and machine identities need strong protection because attackers can use legitimate access to move through an environment.
AI Governance
Businesses need visibility into which AI applications and agents are being used and what data and systems they can access.
Automated Response
Organizations need to determine which security actions can safely be automated and which require human approval.
Supply-Chain Security
Third-party software and cloud services can introduce vulnerabilities that are outside an organization’s direct control.
Continuous Monitoring
A rapidly changing threat environment requires security teams to continuously reassess their exposure rather than relying on occasional reviews.
The Bigger AI Security Race
The cybersecurity industry is entering a period in which speed could become one of the most important competitive advantages.
AI can help attackers find weaknesses faster, customize attacks, and automate repetitive tasks. It can also help defenders analyze more information, detect threats earlier, and respond without waiting for humans to complete every step.
That creates an accelerating technological race.
Palo Alto Networks’ InterSECt 2026 event is designed around that race, with the company emphasizing that frontier AI has compressed the exposure window and that network defenses must move earlier in the attack lifecycle. (Palo Alto Networks)
The unveiling of PAN-OS 12.2 Ceres is therefore part of a much larger conversation about what cybersecurity should look like when machines are increasingly attacking and defending other machines.
When Machines Start Moving at Machine Speed
The biggest change brought by AI-powered cyberattacks may not be that attackers suddenly gain completely new abilities.
It may be that existing abilities become dramatically faster, cheaper, and easier to automate.
That changes the economics of cybercrime and the workload of defenders.
A vulnerability that once took substantial expertise and time to discover could potentially be found more quickly. An attack that once required several specialists could increasingly be automated. A security team that relied on manual investigation could find itself overwhelmed by events arriving faster than humans can process them.
That is why the emerging response is moving toward AI-native and increasingly autonomous defense.
Palo Alto Networks’ Ceres announcement captures that shift: cybersecurity is moving away from simply reacting to attacks after they begin and toward identifying exposure, disrupting attacker infrastructure, and applying automated protections before an intrusion can gain momentum. (Palo Alto Networks TechDocs)
The long-term winner in this contest may not simply be the side with the most powerful AI. It may be the side that can combine intelligence, speed, reliable automation, human oversight, and strong security architecture most effectively.